Bucket Management - Quota, WORM, Policy and Lifecycle
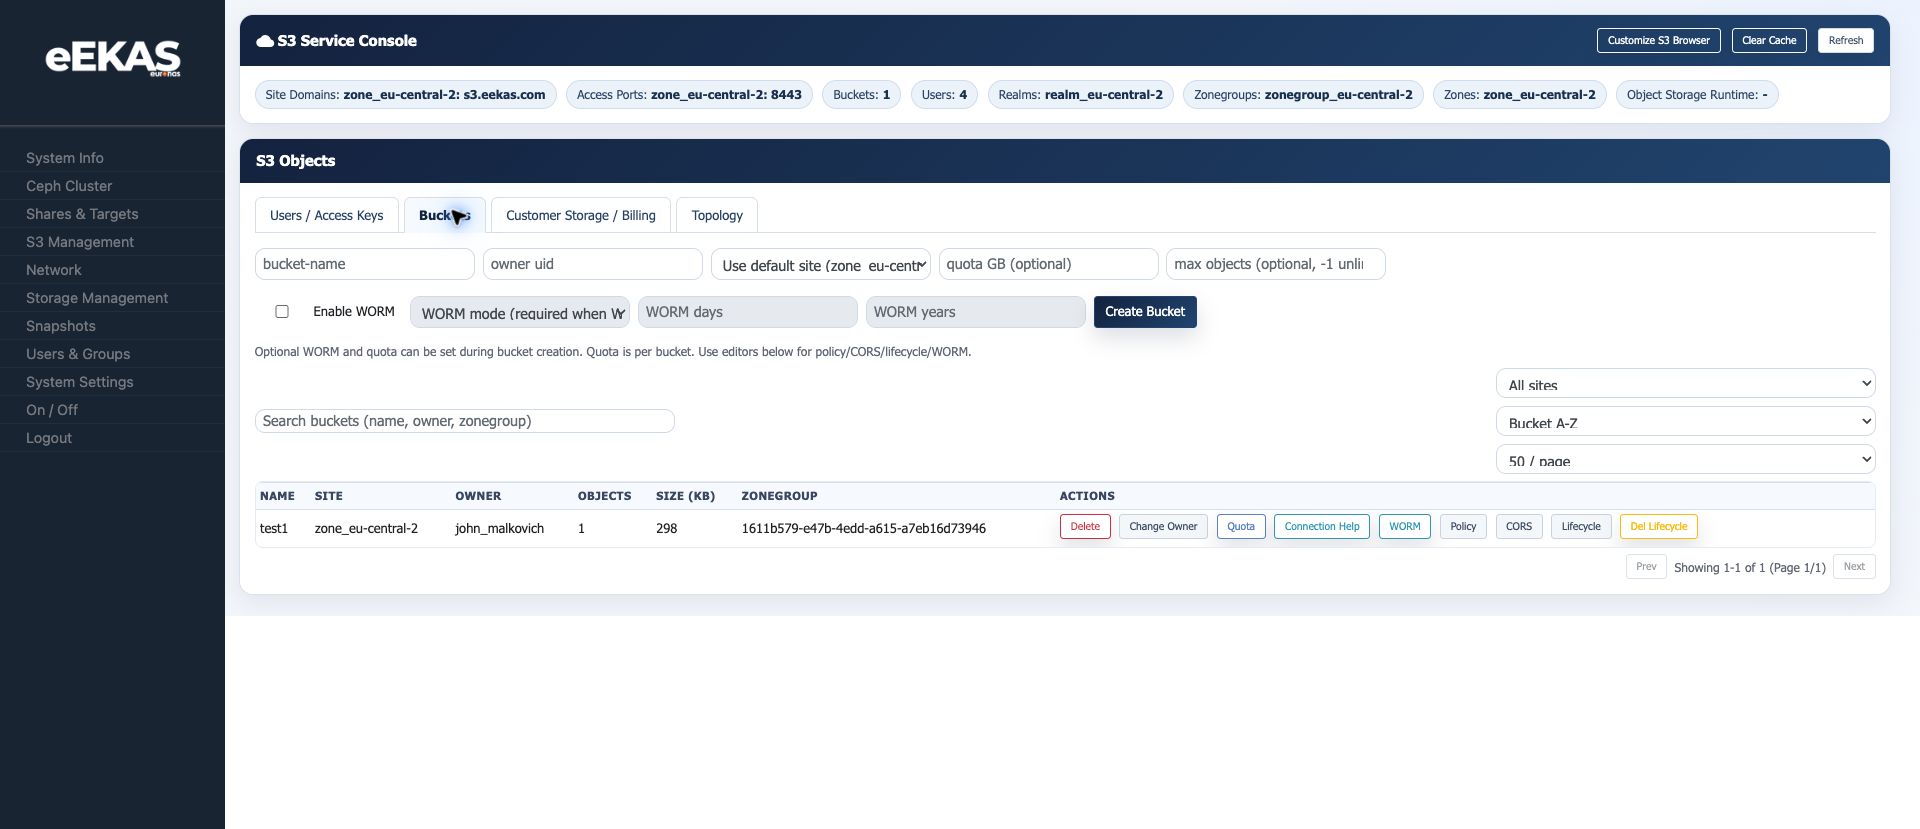
The Buckets tab in the S3 Service Console is the central place for bucket creation and bucket-level controls.
Creating a Bucket
Available creation fields:
| Field | Description |
|---|---|
| Bucket name | Name of the S3 bucket. Use lowercase DNS-safe names for best client compatibility. |
| Owner UID | UID of the S3 user that owns the bucket. |
| Site | Site/zone context for the bucket. |
| Quota GB | Optional capacity quota for the bucket. |
| Max objects | Optional object-count limit. -1 means no object limit. |
| Enable WORM | Creates the bucket with WORM/Object Lock behavior where supported. |
| WORM mode | Retention mode used for protected storage. |
| WORM days / years | Default retention period for protected objects. |
The console note is : WORM and quota can be set during bucket creation. WORM/Object Lock behavior is not just a cosmetic setting; it changes how the bucket can be used later.
Bucket List
The bucket table shows:
- Name
- Site
- Owner
- Object count
- Size
- Zonegroup
- Actions
The bucket list provides actions for delete, owner change, quota, connection help, WORM, policy, CORS and lifecycle.
Quota
Use the Quota action to enable or adjust bucket limits.
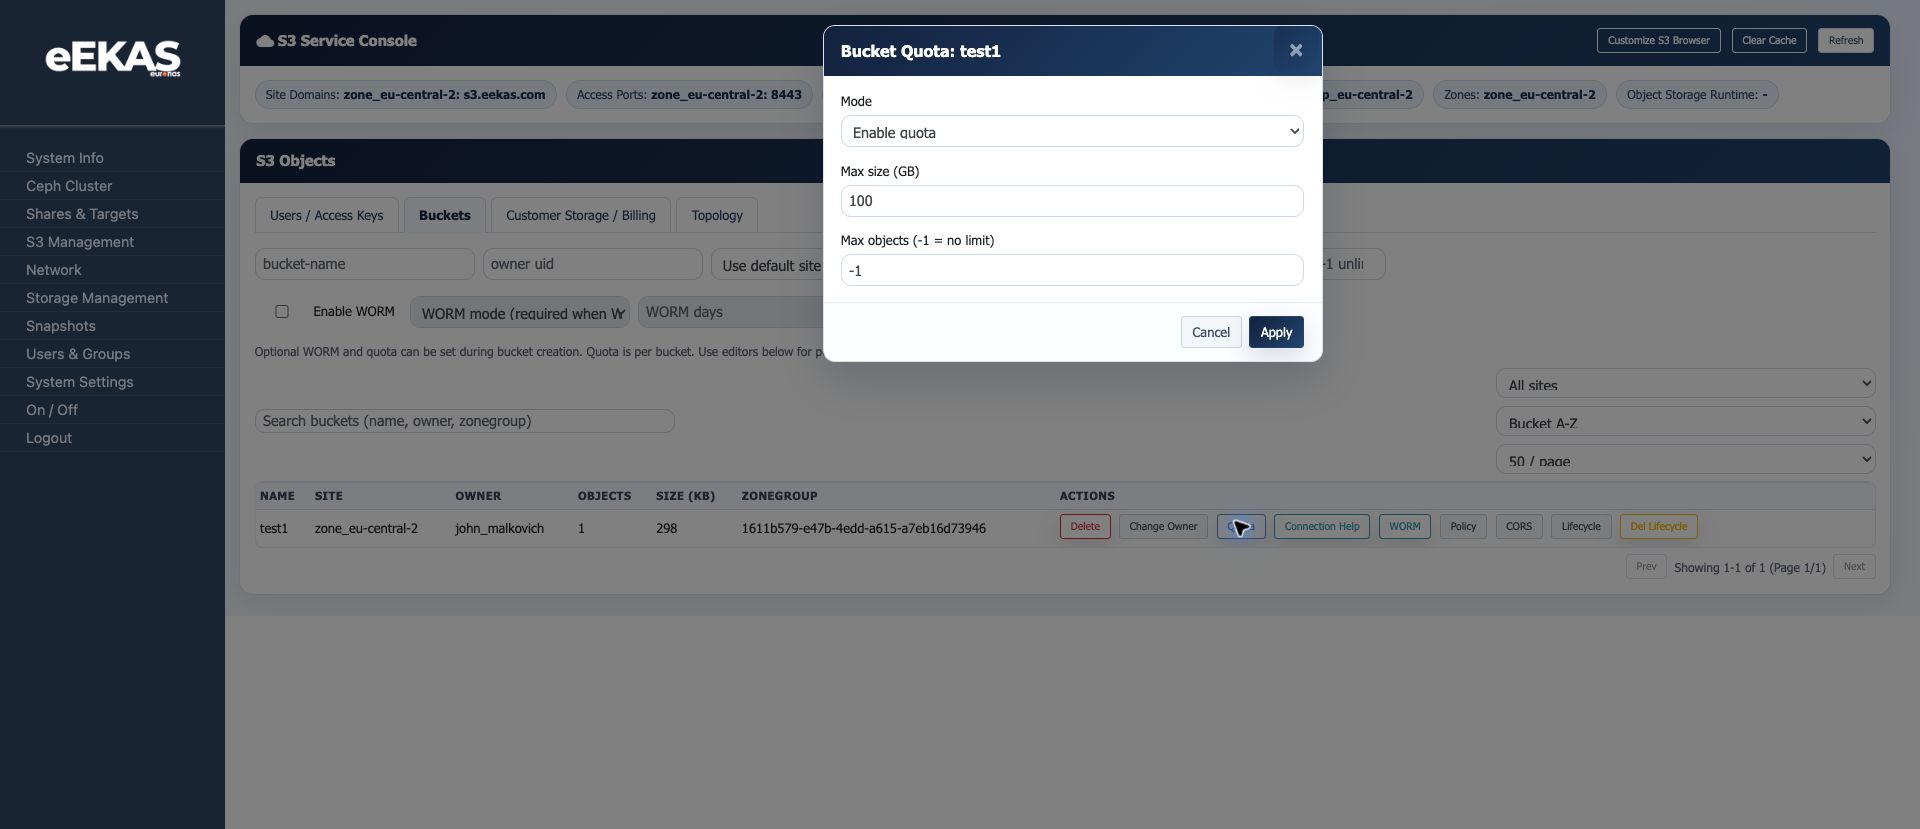
Available settings:
- Mode: enable or disable quota.
- Max size in GB.
- Max objects, where
-1means no object limit.
Quotas are useful for customer storage, backup repositories and multi-tenant services where one bucket must not consume uncontrolled capacity.
Connection Help
The Connection Help action generates user-facing connection information for a bucket.
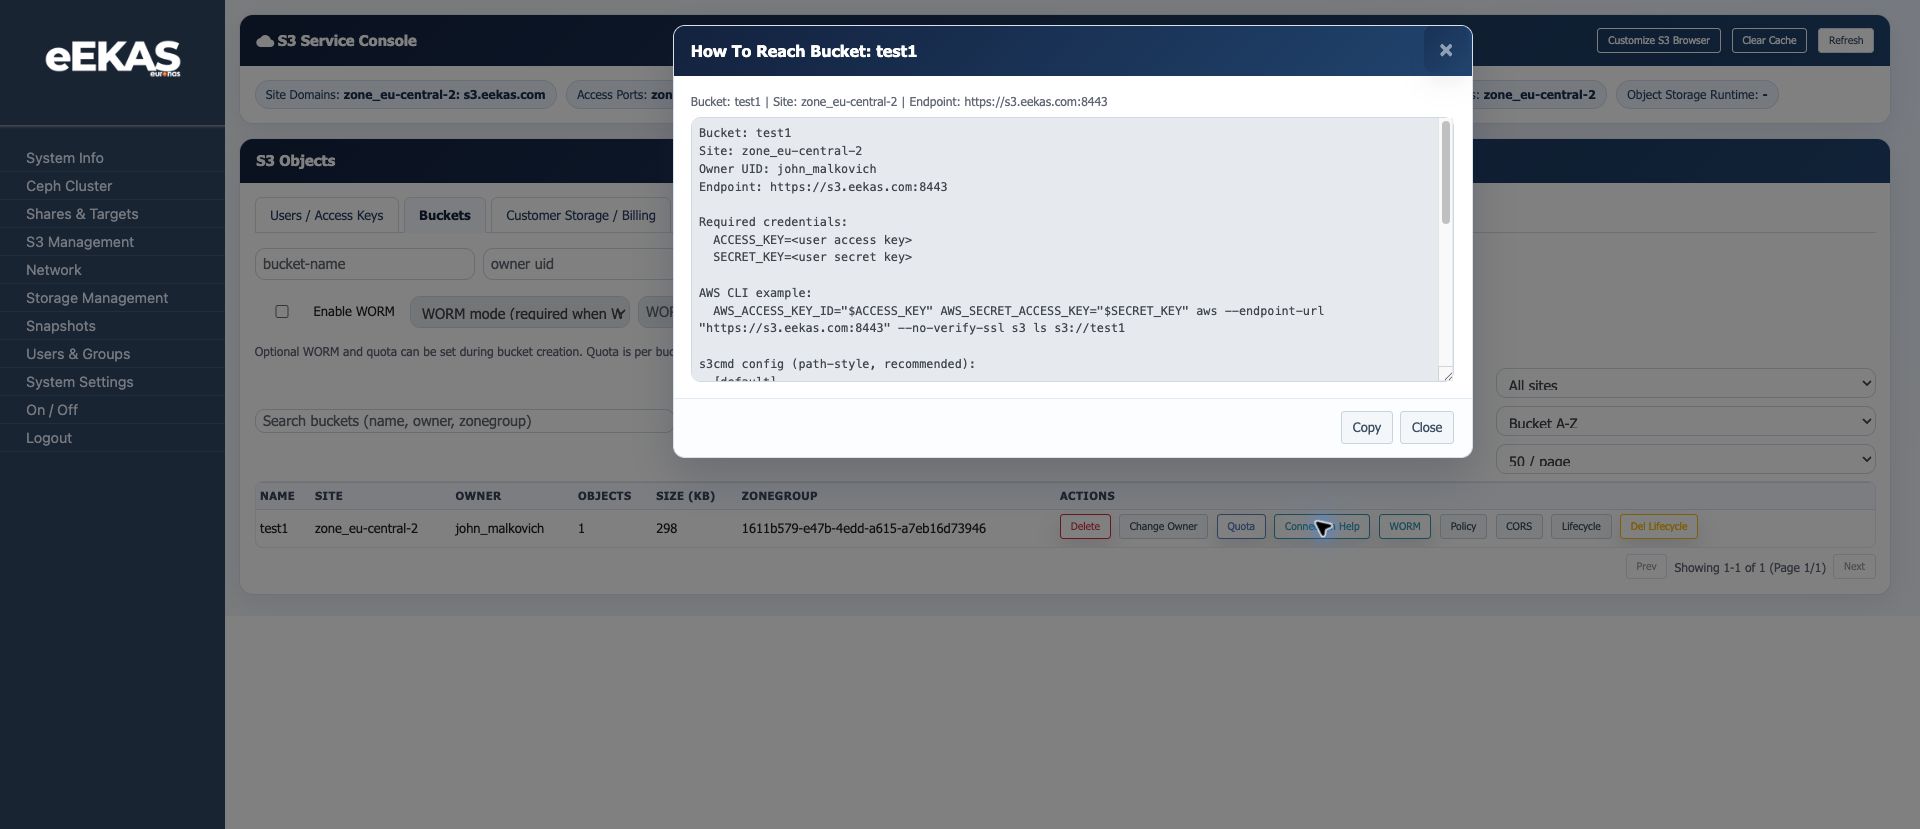
It includes:
- Bucket name
- Site
- Owner UID
- Endpoint
- Required credential placeholders
- AWS CLI example
- s3cmd path-style configuration hints
This dialog is a good source for customer handover instructions. Do not replace the placeholders with real secret keys in public documentation.
WORM and Retention
WORM/Object Lock is used for protected storage and retention-oriented workflows.
Practical notes:
- Enable WORM during bucket creation when the bucket must support protected retention.
- Define WORM mode and default retention period before using the bucket for compliance or backup retention.
- A non-WORM bucket may not expose the same later WORM actions as a WORM-enabled bucket.
- Test restore and delete behavior before using WORM for production compliance workflows.
Policy Editor
Use the Policy action to inspect or edit bucket policy/ACL data.
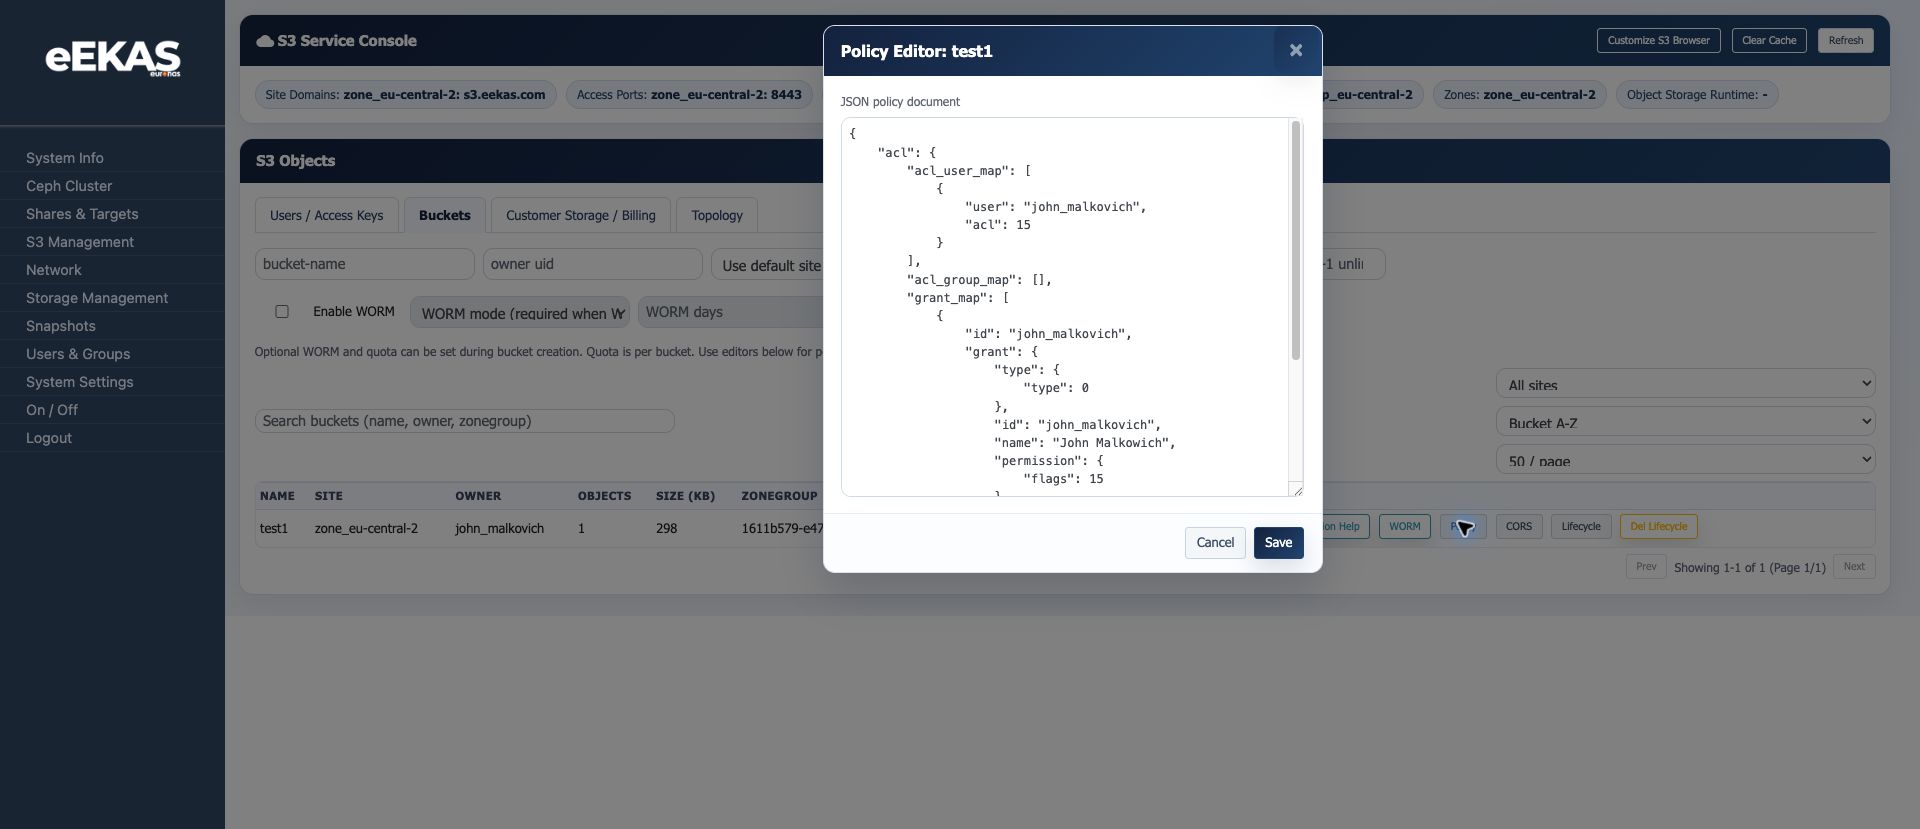
The policy editor exposes JSON policy data. This is powerful but should be handled carefully:
- Keep a copy of the current policy before editing.
- Validate JSON syntax before saving.
- Use least-privilege access rules.
- Avoid granting broad public access unless the bucket is explicitly intended for public content.
CORS
The bucket table exposes a CORS action. Use CORS only when browser-based applications need to access bucket content directly from another origin.
Recommended guidance:
- Keep allowed origins as narrow as possible.
- Avoid wildcard origins for private or authenticated buckets.
- Document which web application requires the rule.
- Test upload, download and preflight behavior after changing CORS.
Lifecycle
Use the Lifecycle action to manage lifecycle policy XML.
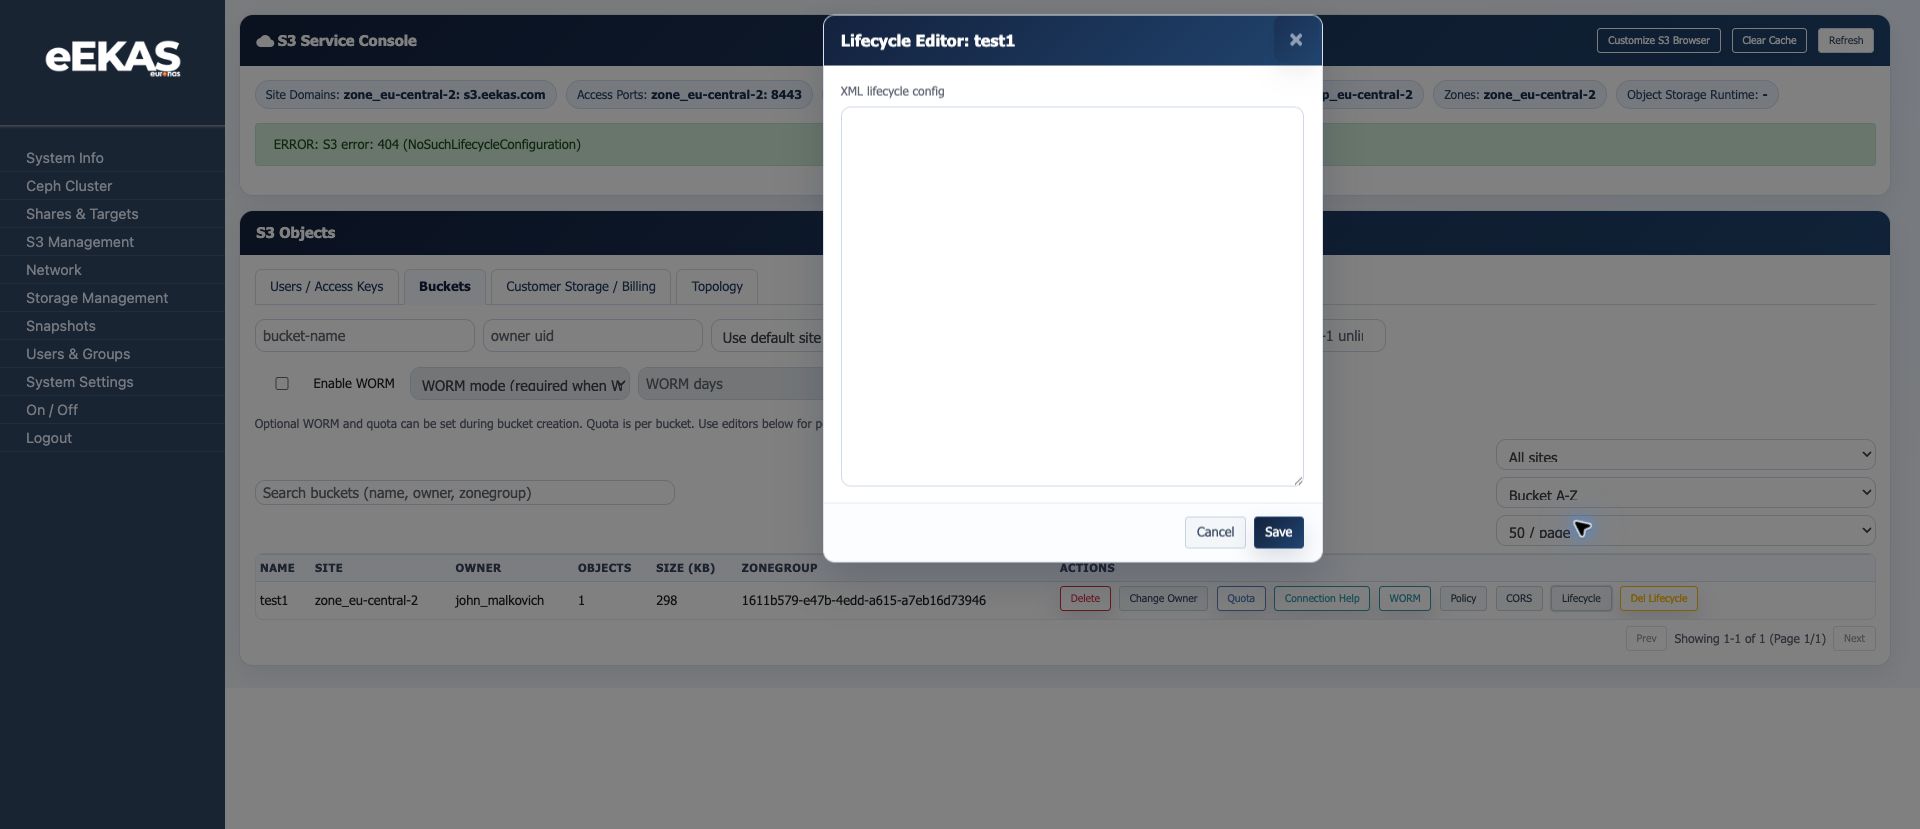
Lifecycle rules are typically used to expire objects, clean up old versions or automate retention-related housekeeping. NoSuchLifecycleConfiguration means that no lifecycle policy is configured.
Before saving lifecycle XML:
- Confirm the intended object prefix or scope.
- Check whether versioned objects are involved.
- Test the rule on a non-production bucket.
- Keep a copy of the XML configuration.
Bucket administration through the API
The 23 October 2026 edition adds POST /api/v1/object-storage/buckets/owner for ownership-change jobs, and GET/PUT operations at /api/v1/object-storage/buckets/versioning and /api/v1/object-storage/buckets/worm. Follow the returned job status_url for an ownership change and verify the resulting owner.
WORM updates require confirmed=true. Use worm_mode=GOVERNANCE or COMPLIANCE and exactly one of worm_days or worm_years. clear_default=true clears the default only: existing protected objects keep their retention. Versioning and WORM changes remain subject to the same protection checks as the GUI.
S3 WORM SMB mappings can be listed, created, updated and removed through /api/v1/object-storage/worm-smb. Check /worm-smb/preflight and /worm-smb/identities before configuring access. Use the installed API specification for required fields and read the SMB WORM guide before changing a mapping.
S3 service health and configuration
GET /api/v1/ceph/storage/overview reports Ceph health, capacity, OSDs and pools. GET /api/v1/observability/ceph provides retained history for ranges 1h, 6h, 24h, 7d, 30d or 90d. Missing metrics are unavailable, not healthy zero values.
GET/PUT /api/v1/ceph/storage/s3-certificate and /api/v1/ceph/storage/s3-ip-group inspect or change S3 certificate and IP-group configuration. Changes require confirmation and return jobs. Send certificates and private keys in JSON request bodies; certificate inspection never returns a private key. Poll completion and verify service connectivity.